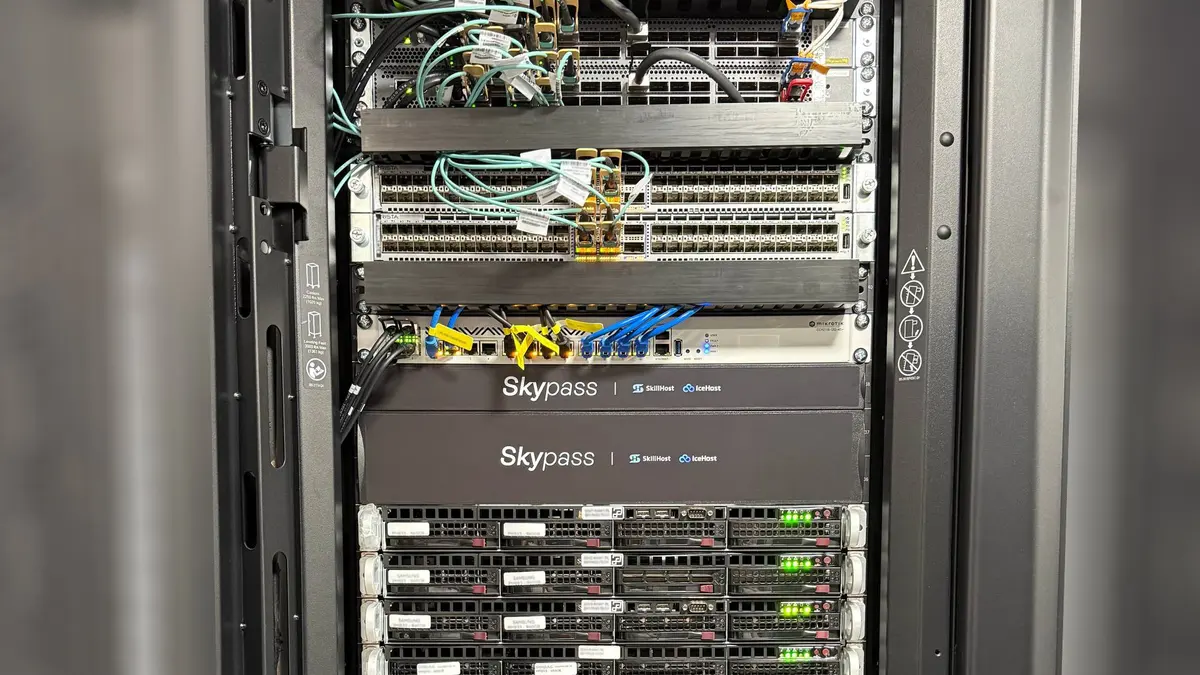
SkyGuard DDoS protection
Attack filtering in Poland, without cutting off your addresses.
- L3/L4/L7 filtering without blackholing
- Scrubbing in Warsaw and Wrocław
- Protection for hosting and carrier networks
An infrastructure partner for ISPs, hosting providers and businesses
We protect against DDoS attacks on our own network and take over care of your IT. We match the connection, protection and scope of support to your infrastructure.
AS202520
Our own network
Open peering policy and presence at Polish internet exchange points.
2
Scrubbing centres in Poland
Warsaw · Wrocław, linked by three independent routes.
400 Gbps
Clean bandwidth after filtering
From 100 Mbps to 400 Gbps, sized to the customer's traffic.
9 Tbps
Largest attack mitigated
Absorbed on our infrastructure without blackholing customer addresses.
How it works
We announce your prefixes from the SkyPass network, so all traffic, including an attack, reaches us first.
Scrubbing clusters filter traffic at layers L3/L4/L7 and drop the attack in real time, without blackholing your addresses.
Cleaned traffic returns to you over a tunnel, a BGP session or a direct link.
Why SkyPass
Check the network in PeeringDB and Looking Glass, and see how the protection performs in the client panel.
Our own AS, scrubbing clusters and NOC. When a problem sits between services, you do not have to reconcile several vendors.
We have been protecting game servers for years, which is why we tune filtering profiles to specific games and protocols.
After an attack you receive a report, and the panel keeps the attack history and a downloadable tcpdump capture.
You test SkyGuard on your own traffic, without affecting production, before you sign a longer contract.
Hardware and technologies we use
Anycast network
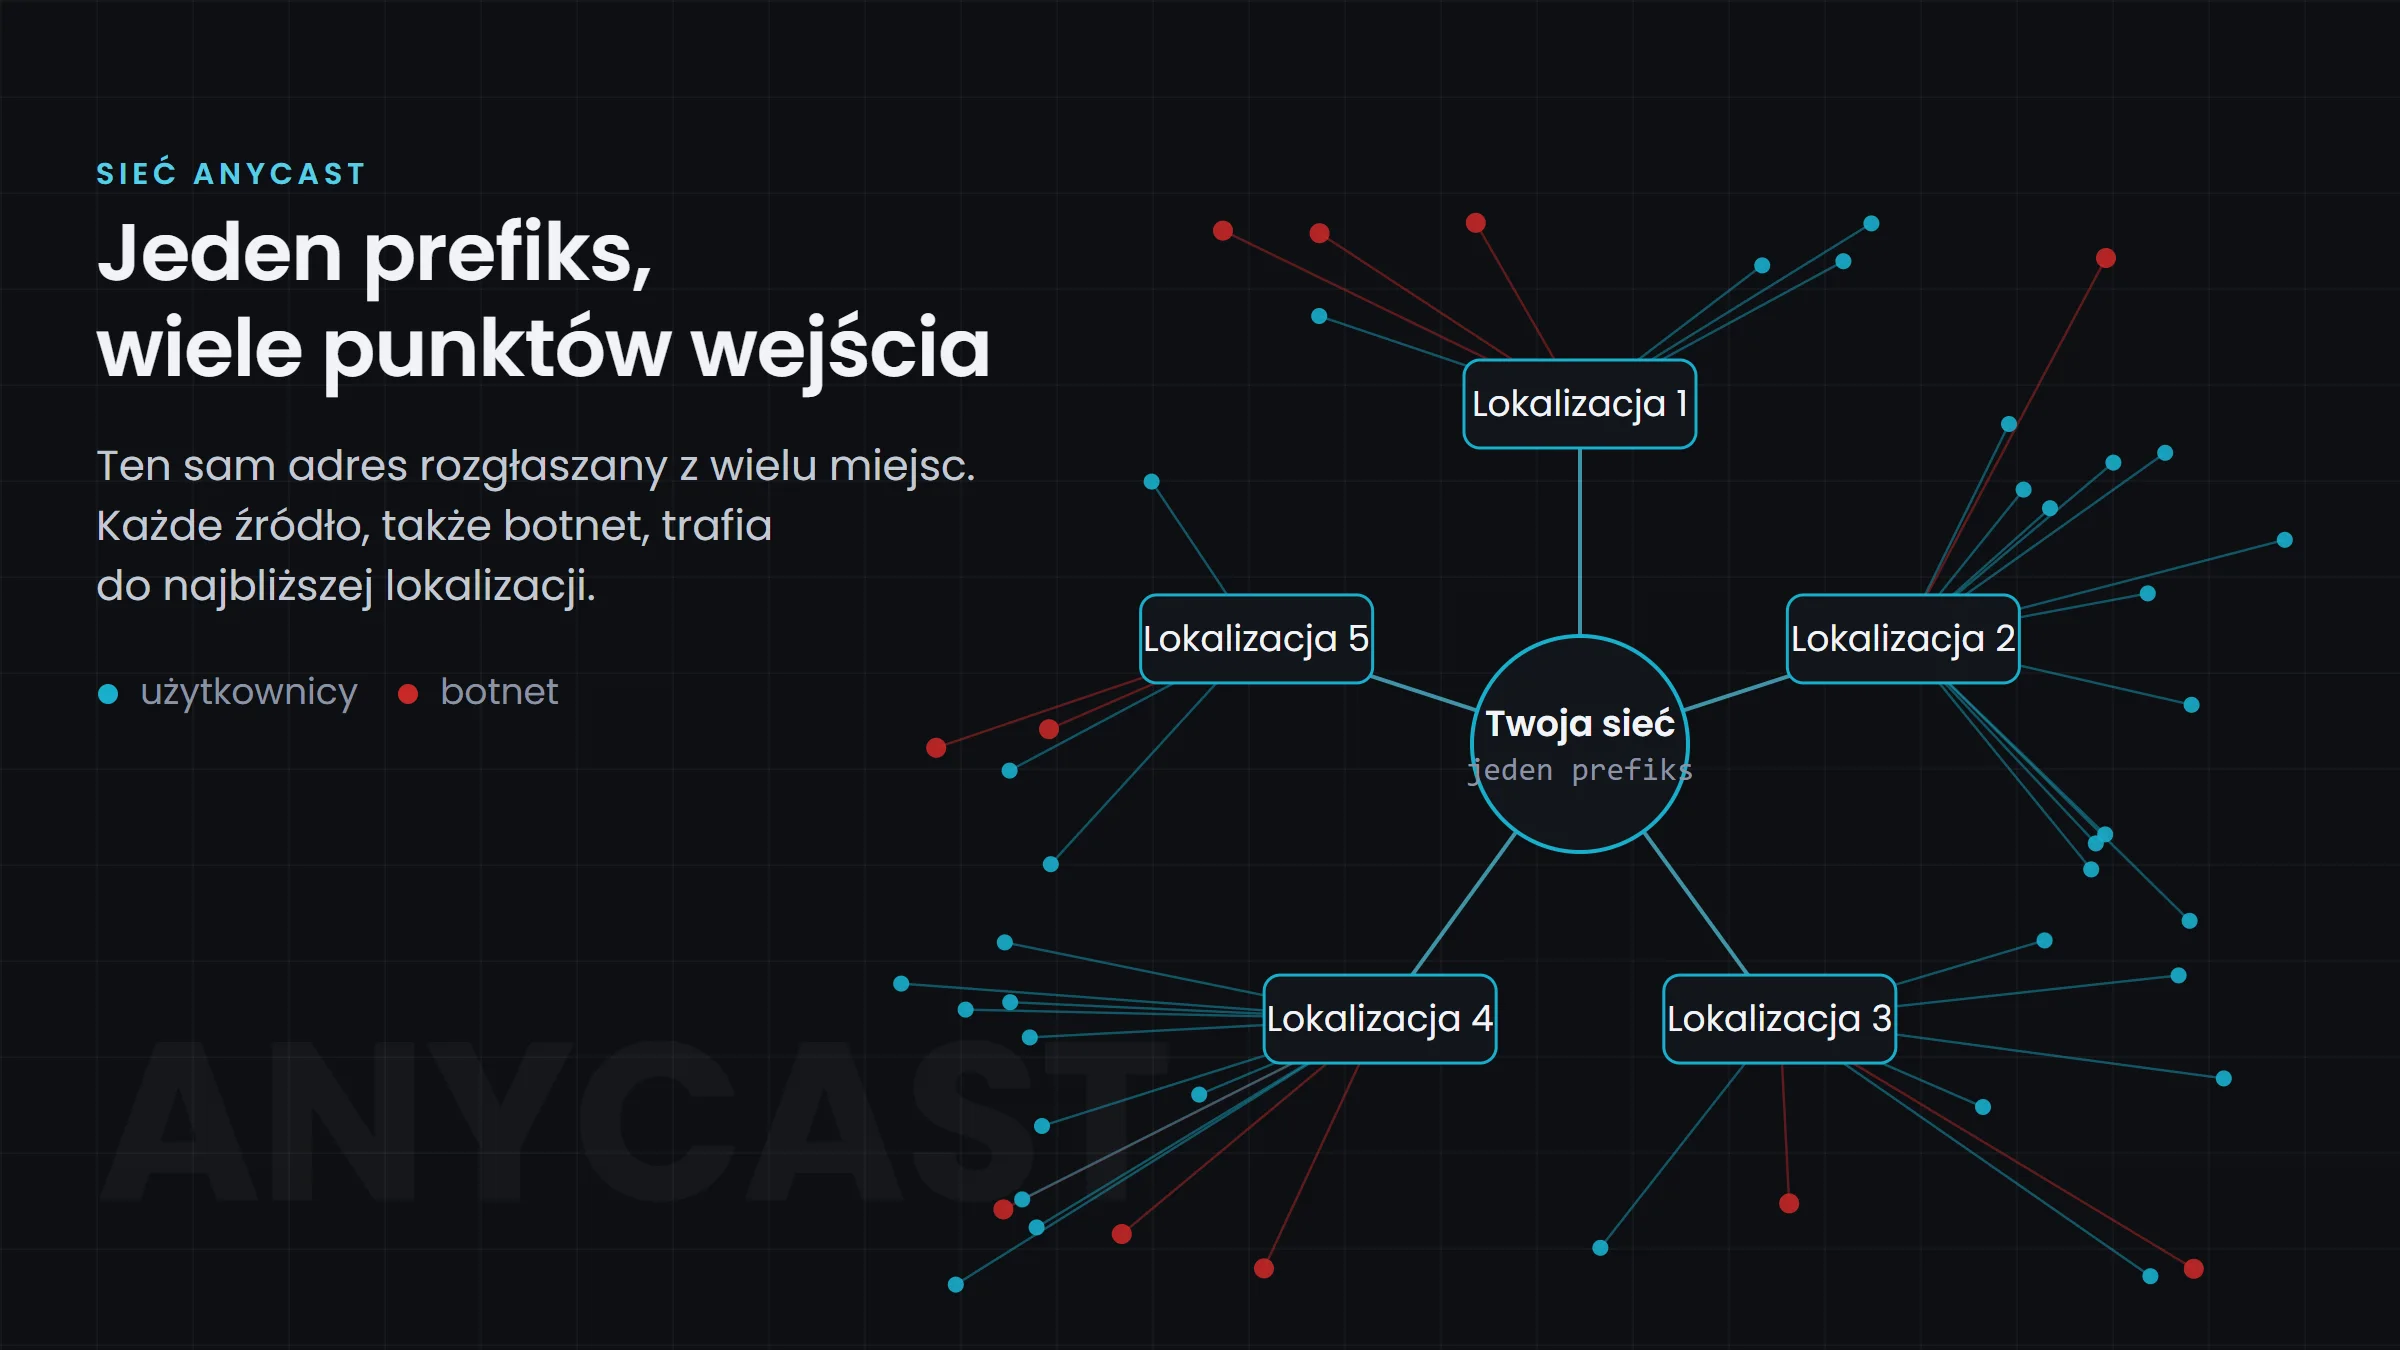
Our network is anycast in many locations, so an attack does not hit a single place but is spread over many entry points.
Traffic from different directions enters the network in different places.
Part of the attack is dropped close to the source, not at one central point.
Each location takes only a fraction of the attack volume.
IceHost (Minecraft servers) and SkillHost (VPS, VDS and dedicated servers) run on the same network and protection every day.


Solutions
DDoS protection, our own network and care for your company's IT from one partner.
Attack filtering in Poland, without cutting off your addresses.
Connect to the SkyPass network remotely or physically in the data centres.
On site in Wrocław and Kraków, remotely across Poland and the EU.
Trusted in the industry
SkyGuard is used by ISPs and hosting brands for which downtime during an attack is a real loss. Instead of logos, we show what you can verify yourself.
Carrier networks with BGP integration and per-prefix policies. Customers see how well the filtering works on their own graphs.
Filtering profiles for game engines and protocols.
Open peering, presence at Polish internet exchanges and a public AS202520 record in PeeringDB.
How we start
We start from your infrastructure and requirements, not from a price list.
We get to know your topology, peak traffic and requirements, then propose a protection variant or a scope of IT support with an offer.
We set up tunnels, BGP sessions and filtering policies, or take over your IT in stages. We run tests without affecting production.
Active protection with 24/7 NOC monitoring, or ongoing IT care with regular reports.
You can test SkyGuard protection on your own traffic before signing a longer contract.
FAQ
Answers for the people who decide on the budget and for the engineers who will implement it.
Blog
We write about networking, DDoS protection and infrastructure, based on our day-to-day work.
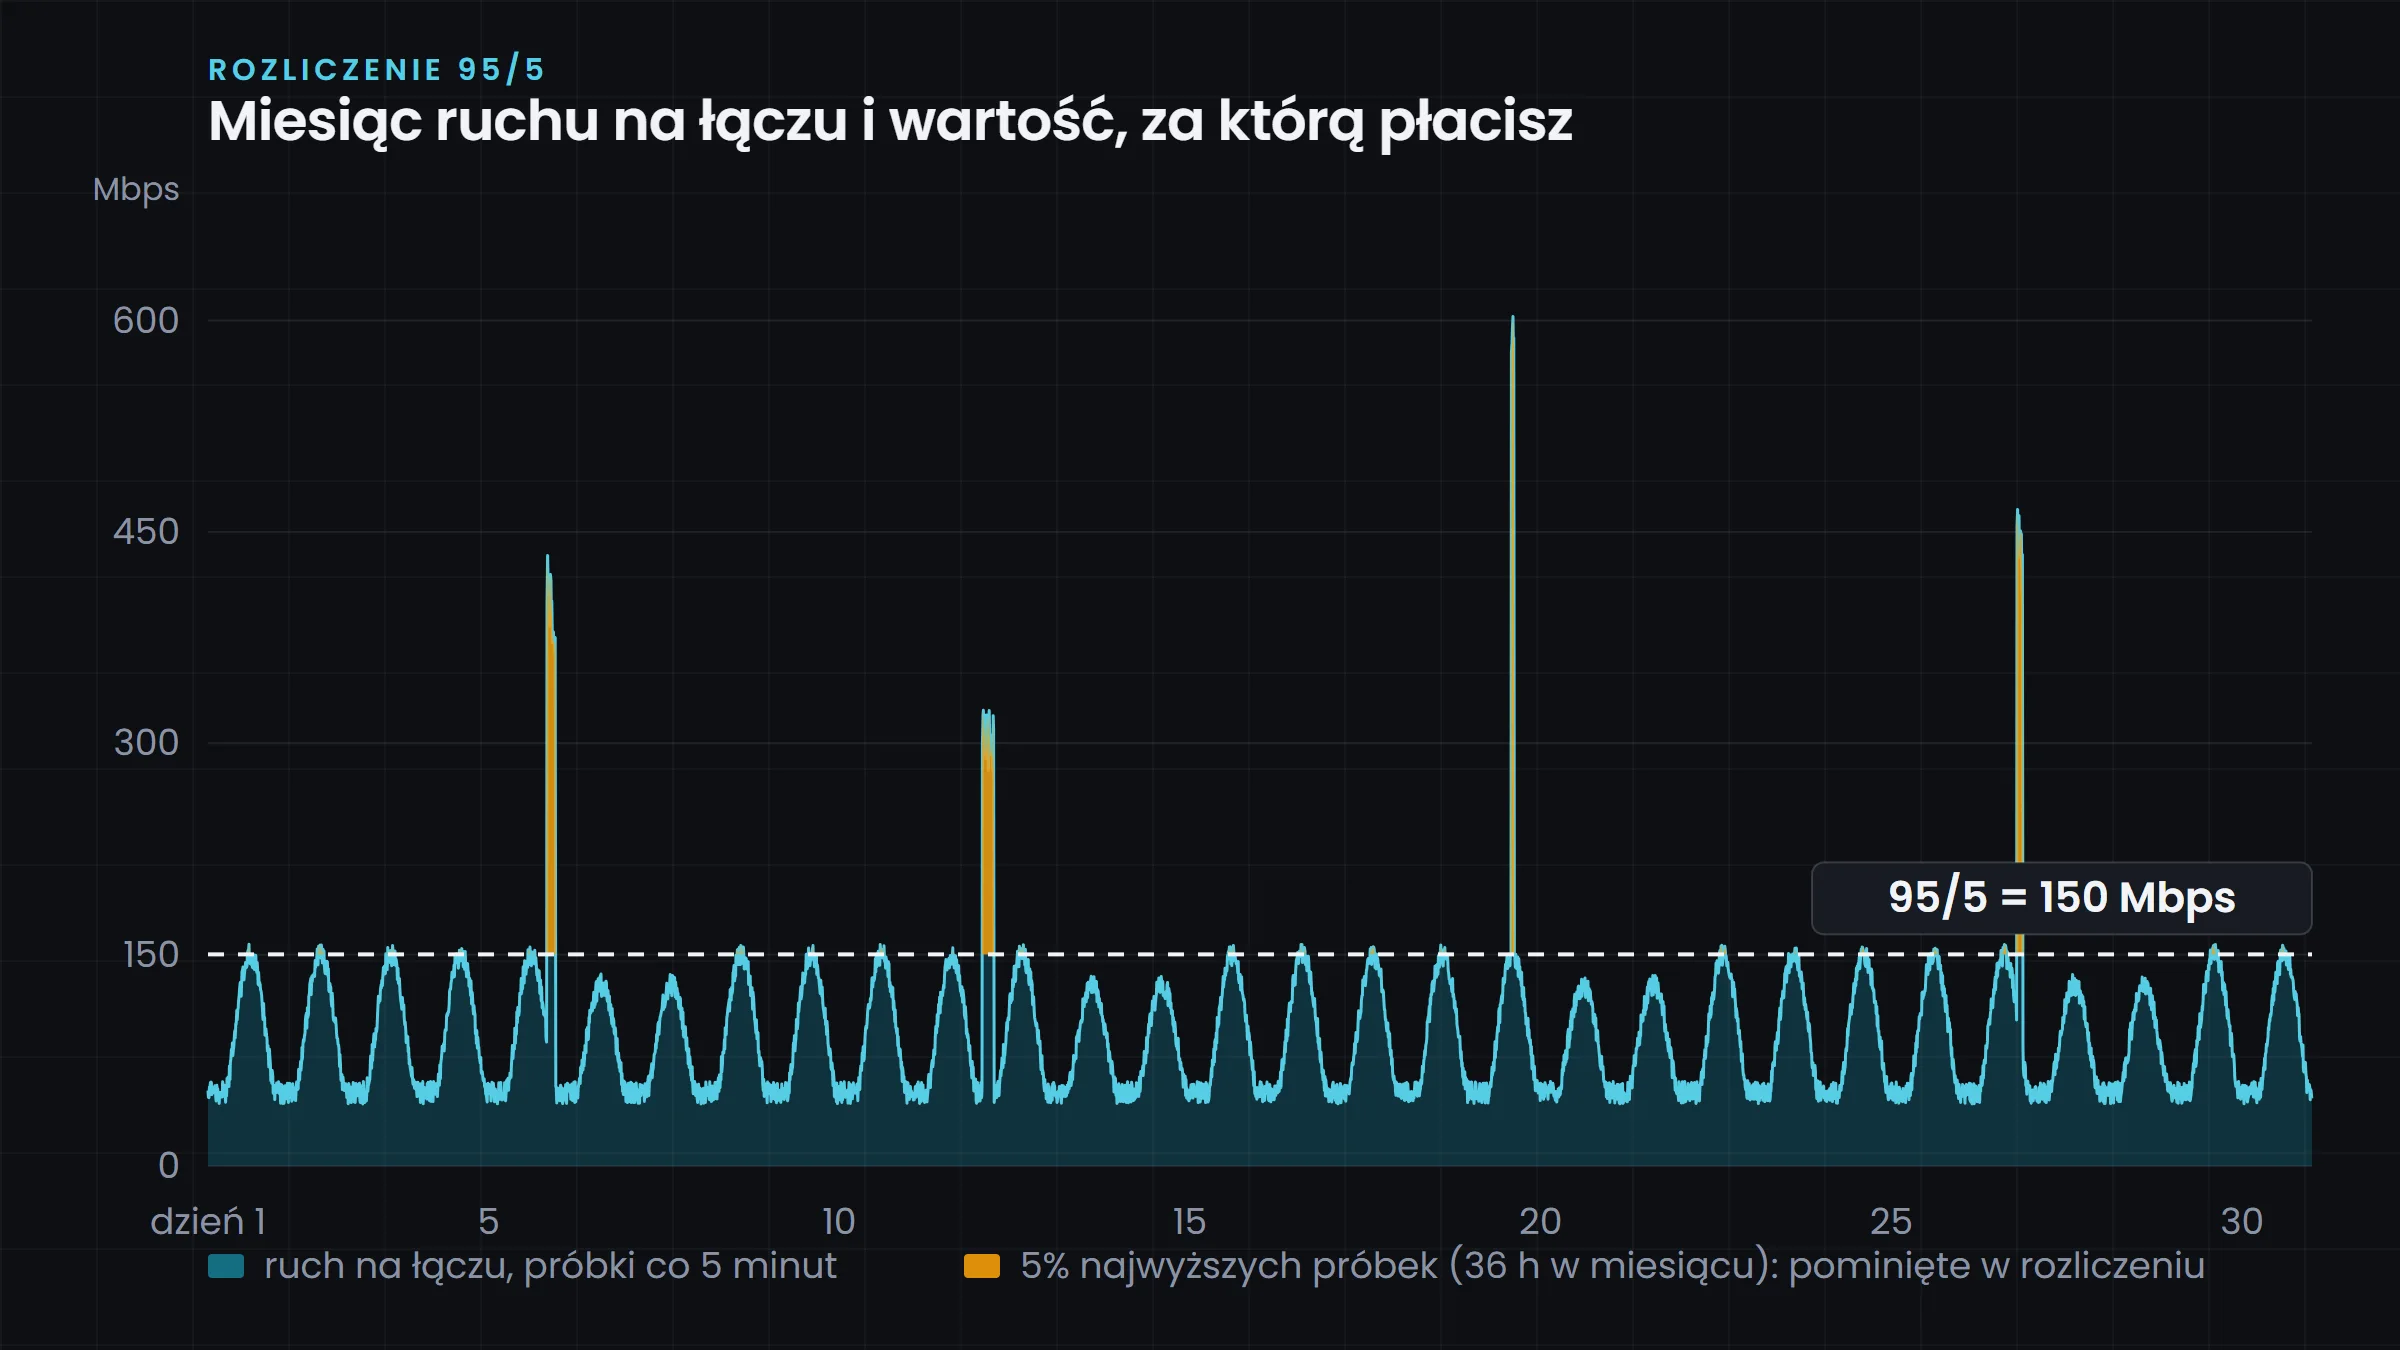
7 min readpl
Jak operatorzy liczą 95. percentyl łącza, ile godzin szczytu w miesiącu nie wchodzi do rachunku i kiedy 95/5 opłaca się bardziej niż rozliczenie po transferze albo stałe pasmo.
6 min readpl
Jak działa anycast w BGP, czym różni się od unicastu i dlaczego sieć rozgłaszana z wielu lokalizacji przyjmuje atak DDoS lepiej niż pojedynczy punkt wejścia. Zalety, ograniczenia i przykład z sieci SkyPass.
8 min readpl
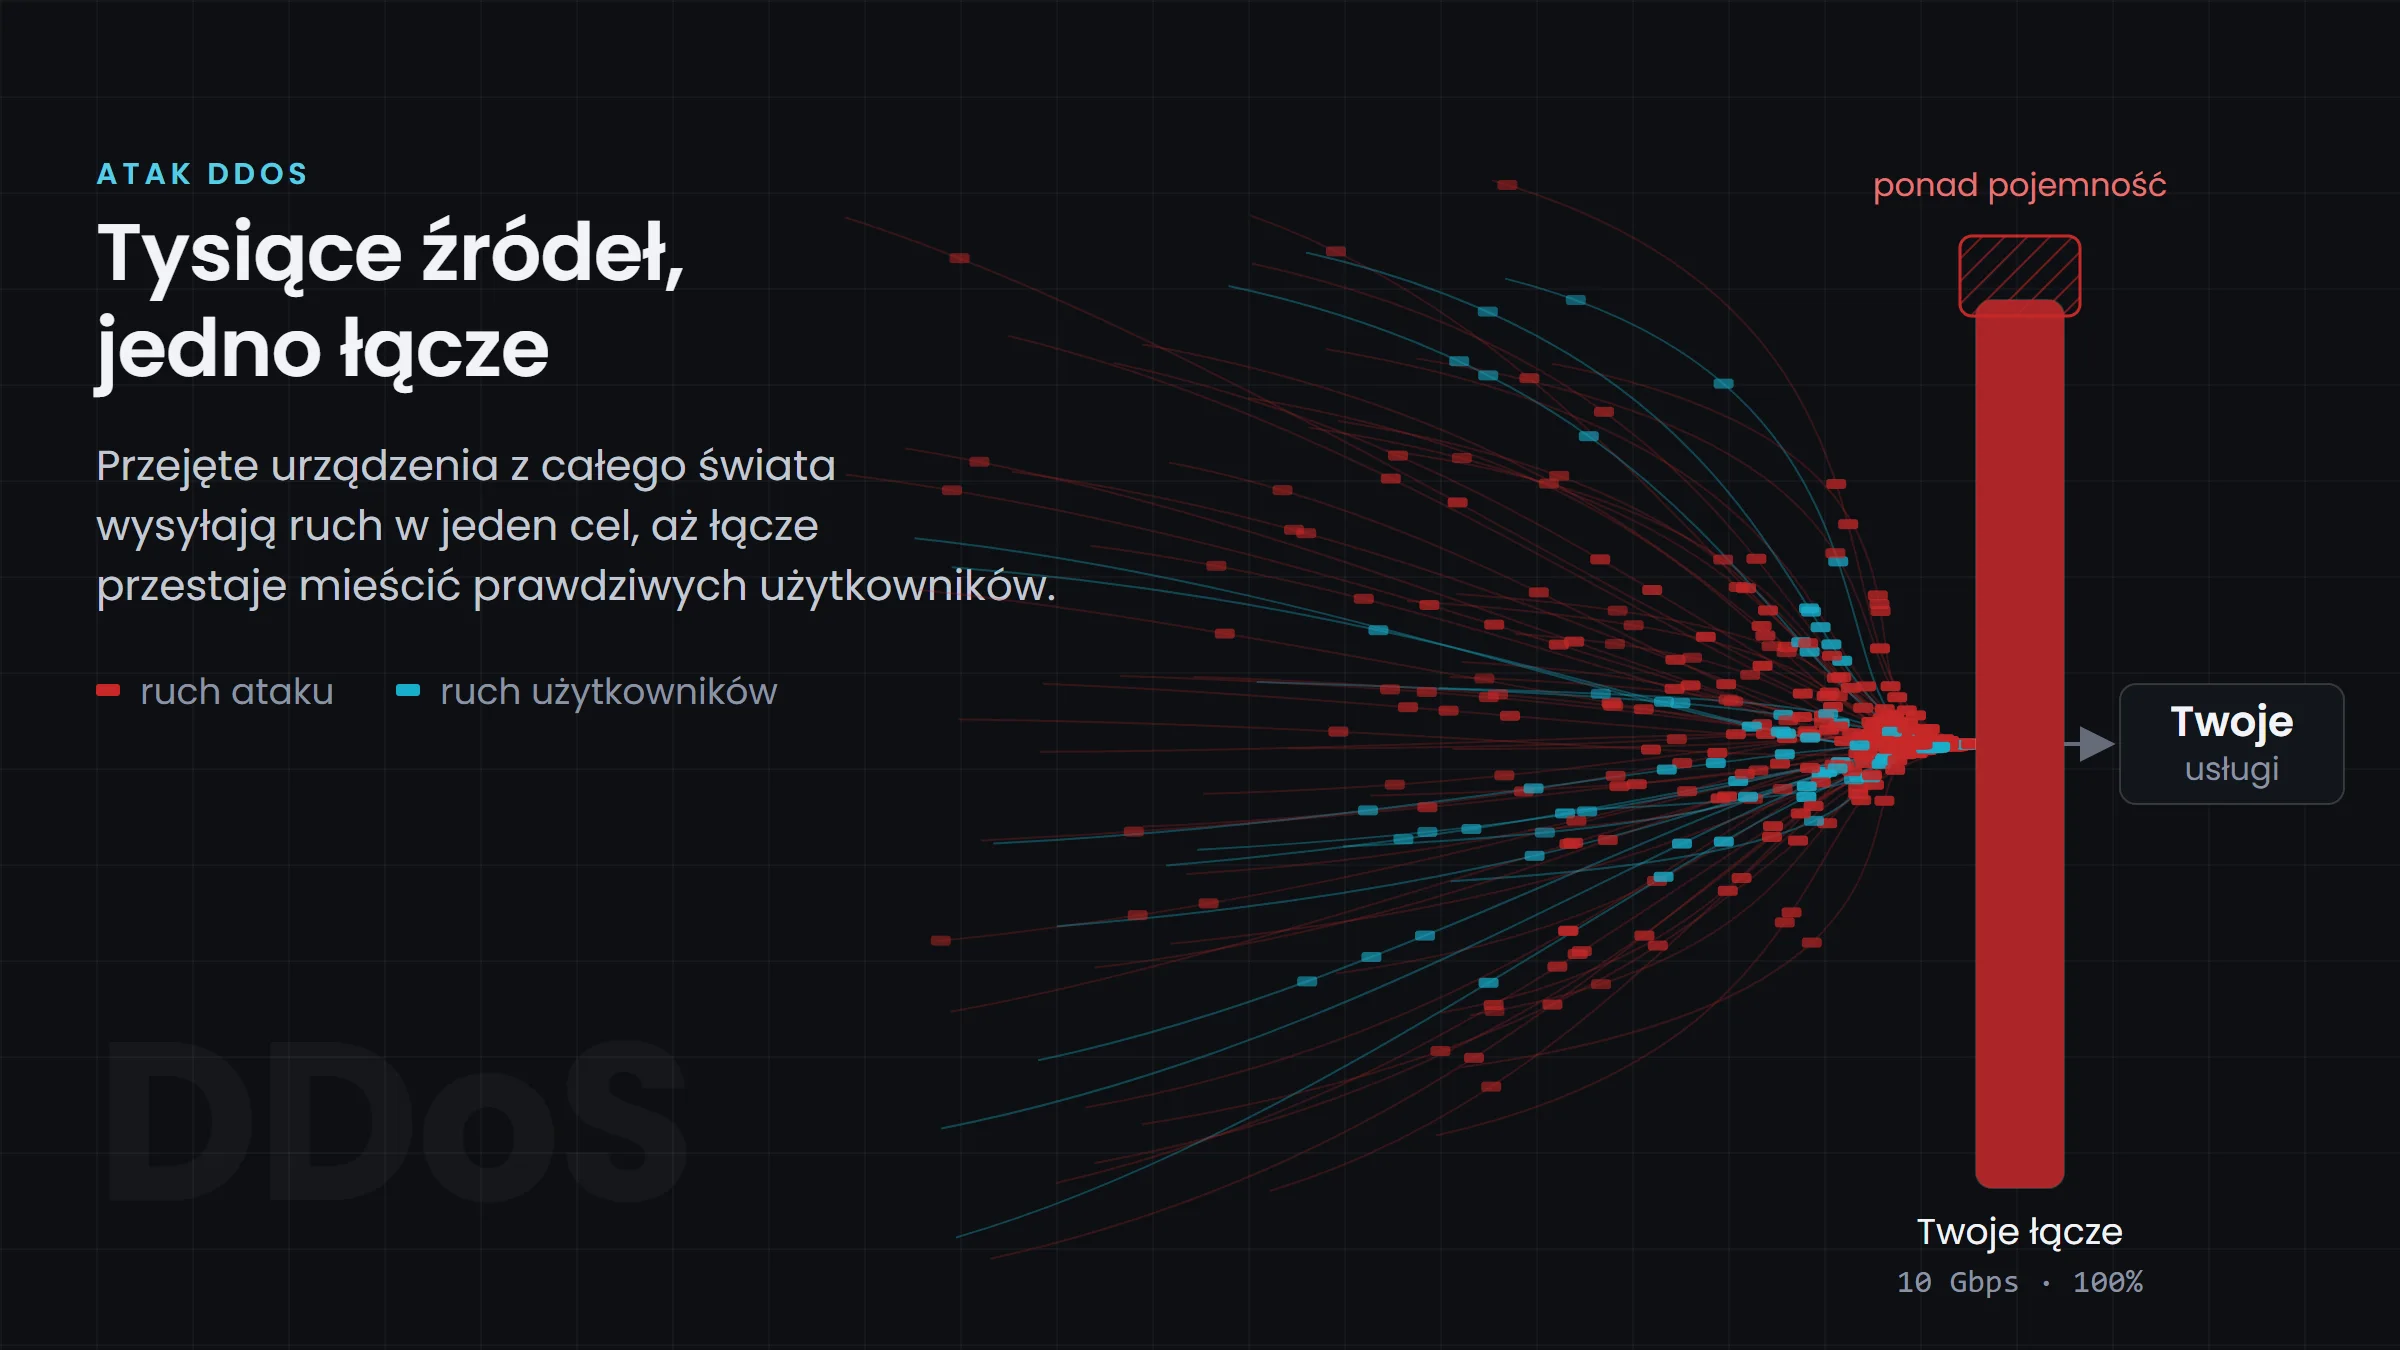
Czym jest atak DDoS, jak działają ataki wolumetryczne, protokołowe i aplikacyjne, ile kosztuje brak przygotowania i co zrobić, zanim atak się zacznie. Z przykładem z sieci operatora ISP.
Contact
Describe what you protect or maintain, and we will propose a service variant and connection method.
After you send the form, we come back to you with questions about the details or a proposal for the next step: a call, tests or an offer.